Cyber security & QA services in India
Every build goes through a security and QA pass before launch — and we can audit the software you already run.
Most breaches exploit ordinary mistakes: injectable queries, exposed secrets, weak access rules and outdated dependencies. We find and fix them before attackers or customers do.
Security and QA are part of how we deliver every product, and we also offer them as a standalone service for existing websites, apps and APIs.
What we build
Security audits
Reviewing code, configuration and infrastructure for vulnerabilities.
Penetration testing
Testing your application the way an attacker would.
Dependency & secret scanning
Finding vulnerable libraries and exposed keys.
QA & testing
Functional, regression and device testing before every release.
Performance testing
Making sure systems stay fast under real load.
Remediation
Fixing what we find, not just reporting it.
- OWASP
- Static analysis
- Dependency scanning
- Automated testing
Recent work
- GeM Consulting Portal
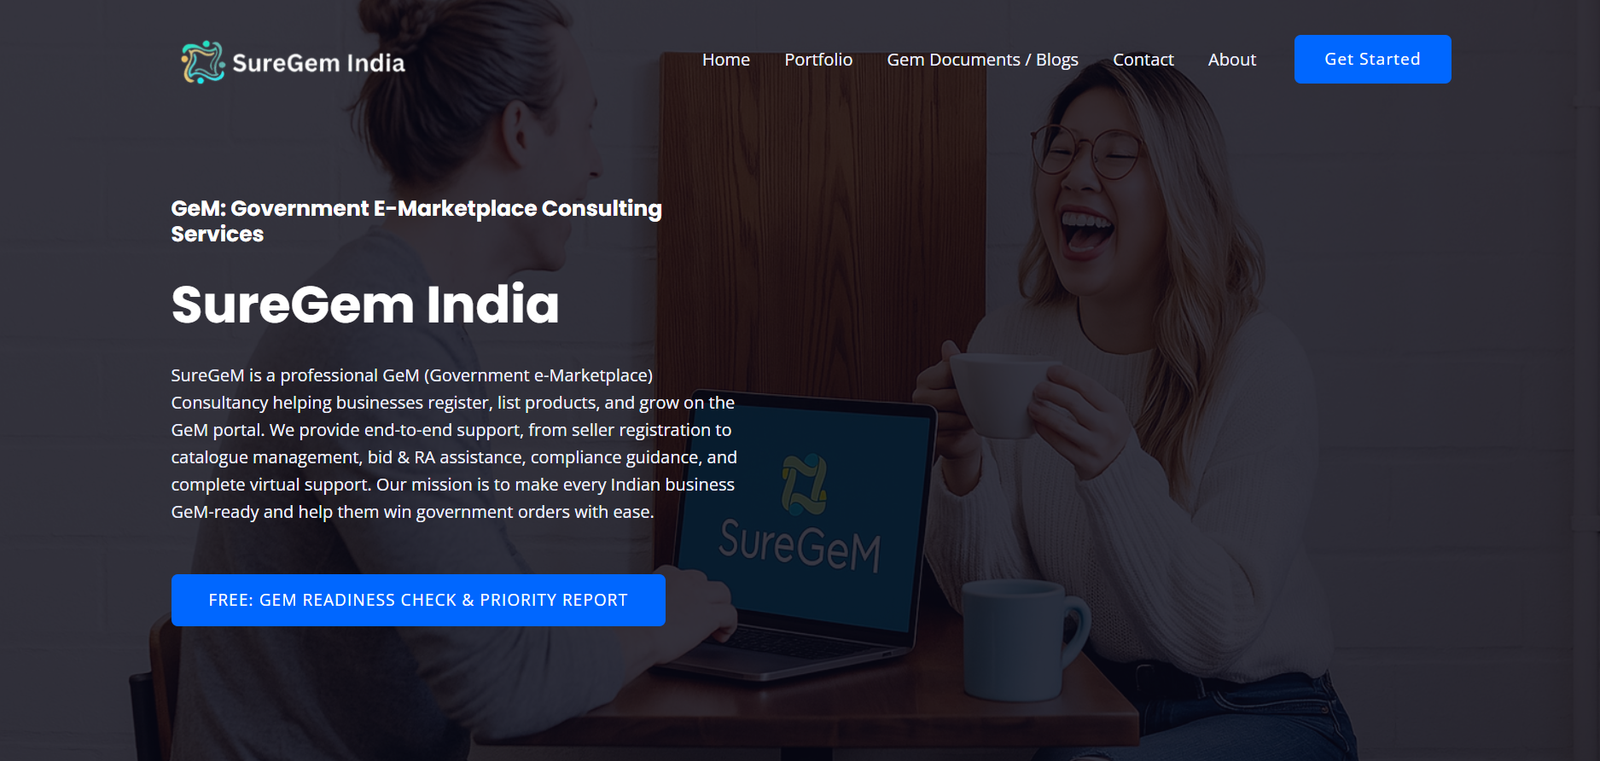
SureGeM India
Government e-Marketplace (GeM) consulting portal with a conversion-focused funnel that tripled inbound inquiries in month one.
Read the case study →
How we work
- 01
Brief
A short call to understand your business, your users and what success looks like. We scope the real problem before touching a single pixel.
- 02
Build
Design and development run in tight loops — you see working previews every few days, not a single reveal at the end of the project.
- 03
Launch & Grow
We ship, monitor and iterate. Every product we hand over comes with the code, the ownership, and a plan for what comes next.
- You own the full source code
- Direct access to the people building it
- Fixed scope, fixed price — no surprise invoices
- Working preview within days, not months
- Post-launch support included
- Built on modern, maintainable stacks
- SEO & performance baked in from day one
- No lock-in to a proprietary platform
Frequently asked questions
Can you audit a website or app you didn't build?
Yes. We audit existing websites, apps and APIs and help your team fix what we find.
What do you check in a security audit?
Common vulnerability classes such as injection, cross-site scripting, broken access control, exposed secrets and outdated dependencies, plus configuration and infrastructure.
More services
Ready to start your cyber security & qa project?
Tell us what you're building — we reply within 24 hours with next steps.
Talk to GOBT